Risk Management
Basic Approach to Risk Management
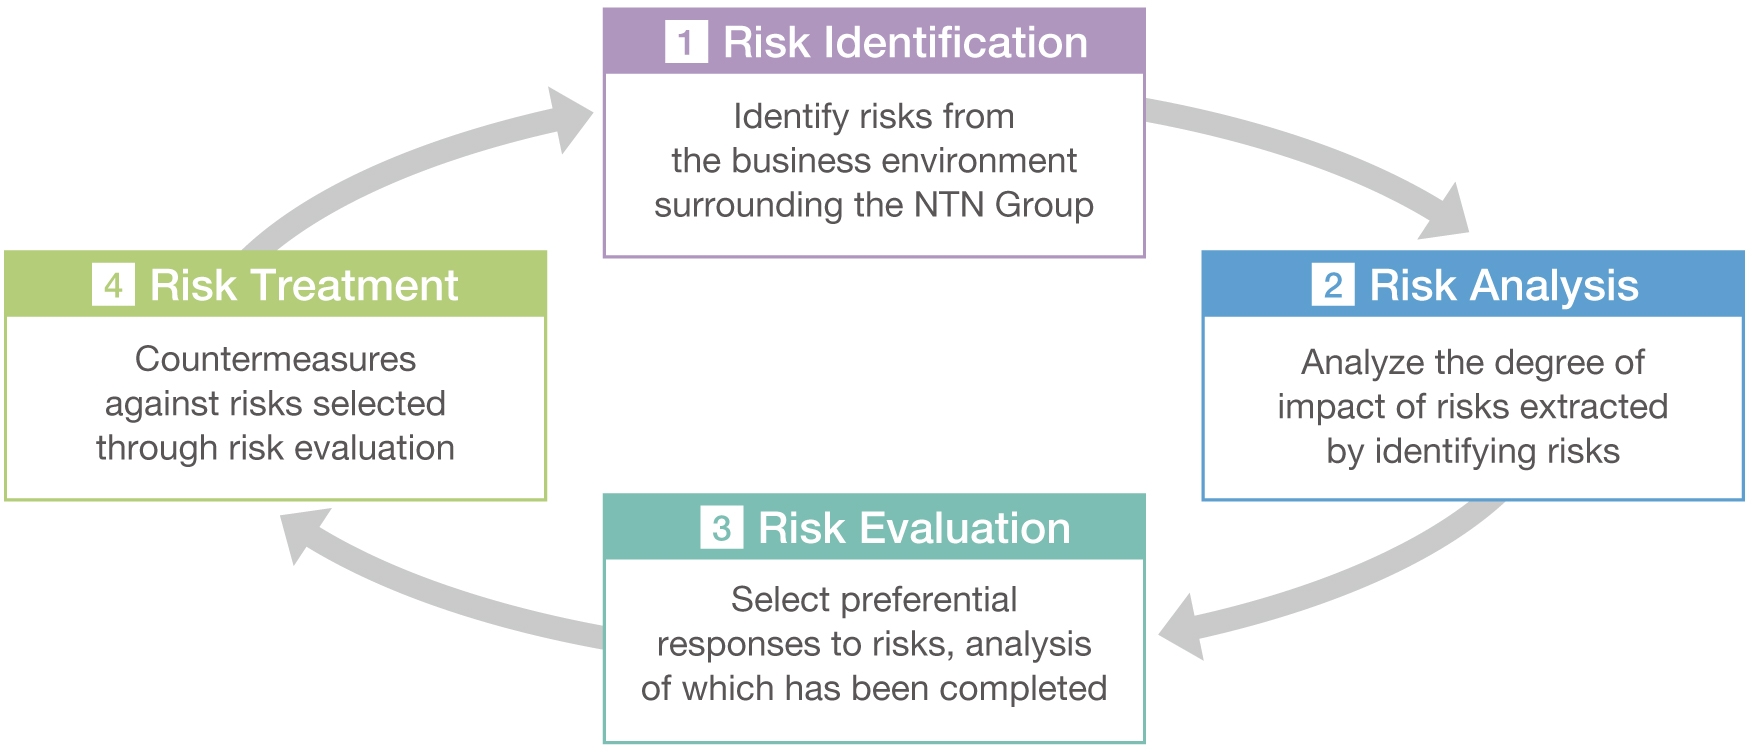
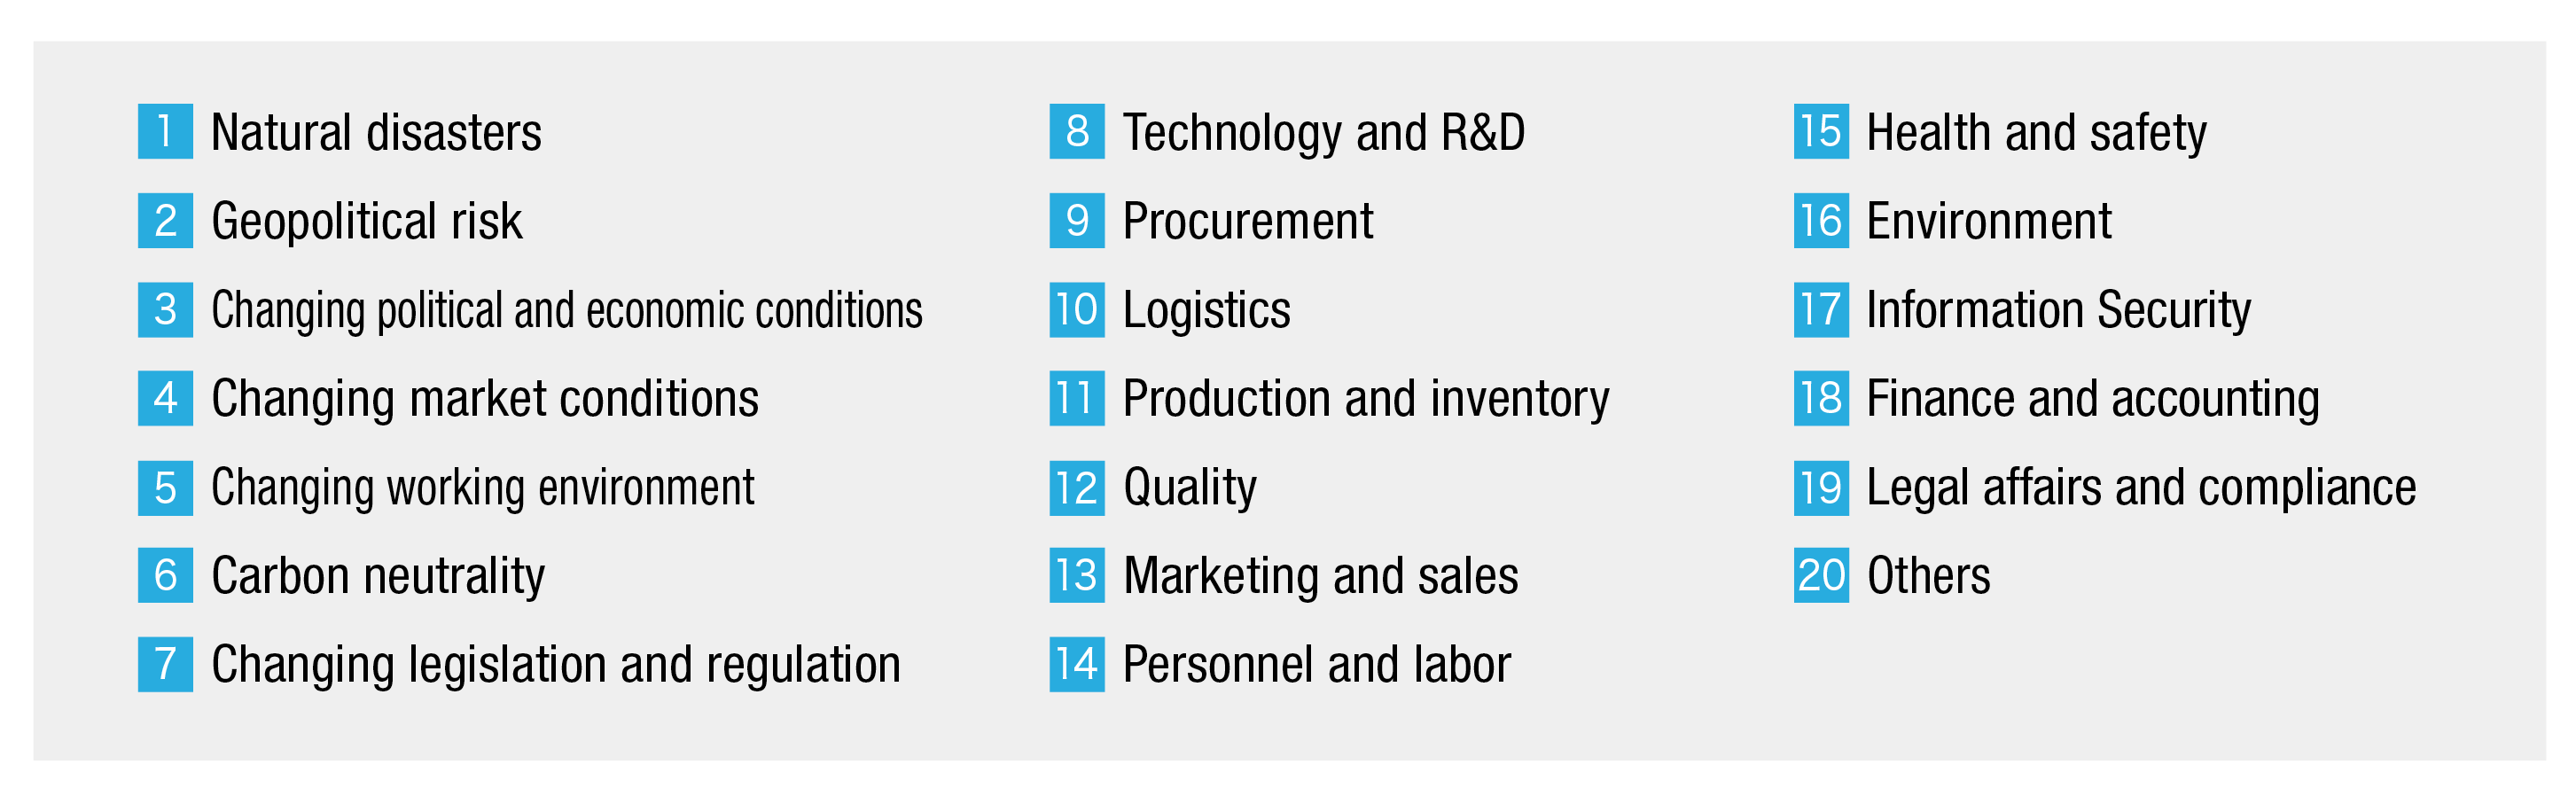
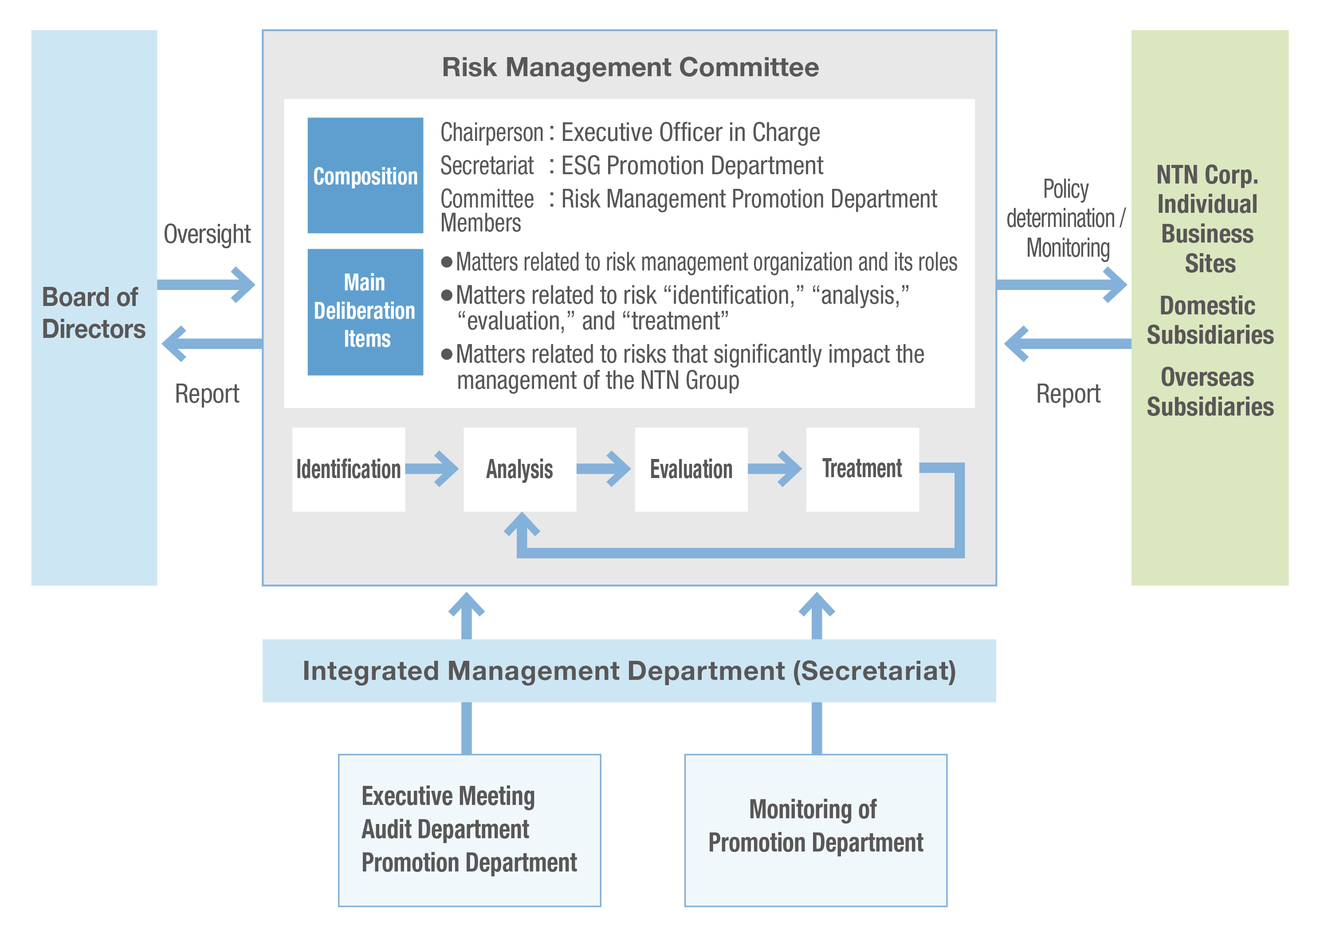
The NTN Group positions the proactive prevention of risks that may impede business operations, as well as the ability to respond appropriately when such risks materialize, as a critical management foundation for achieving sustainable business growth and enhancing corporate value over the medium term. Based on this approach, we have established the Risk Management Policy and the Risk Management Regulations, and are promoting risk management and BCP/BCM (Business Continuity Plan/Business Continuity Management) across the entire Group. With the aim of preventing risks and minimizing damage when crises occur, we have established a Risk Management Committee chaired by the Executive Officer in charge of the ESG Promotion Department. The Committee regularly reviews the identification, analysis, evaluation, and treatment of risks that have a material impact on management. Risks are systematically classified into 20 categories, with management personnel and promotion departments clearly defined for each, thereby ensuring effective risk management. The matters deliberated by the Committee are reported to the Board of Directors twice a year, ensuring oversight by management.
■Management process
■Relevant risks
Risk Management Structure
The NTN Group’s risk management structure is headed by the Executive Officer in charge of risk management as the General Manager, and consists of the Integrated Management Department, the Promotion Department, and the Implementation Department. The Integrated Management Department serves as the Secretariat of the Risk Management Committee and centrally oversees the identification, analysis, evaluation, and treatment of risks across the entire Group. The Promotion Department, as the department responsible for risks related to its assigned operations, carries out risk assessments, reports to the Integrated Management Department, formulates relevant regulations and measures, establishes management systems, and provides education and awareness regarding risk management, as well as guidance and advice to subsidiaries.
■Structure
Crisis Management Structure
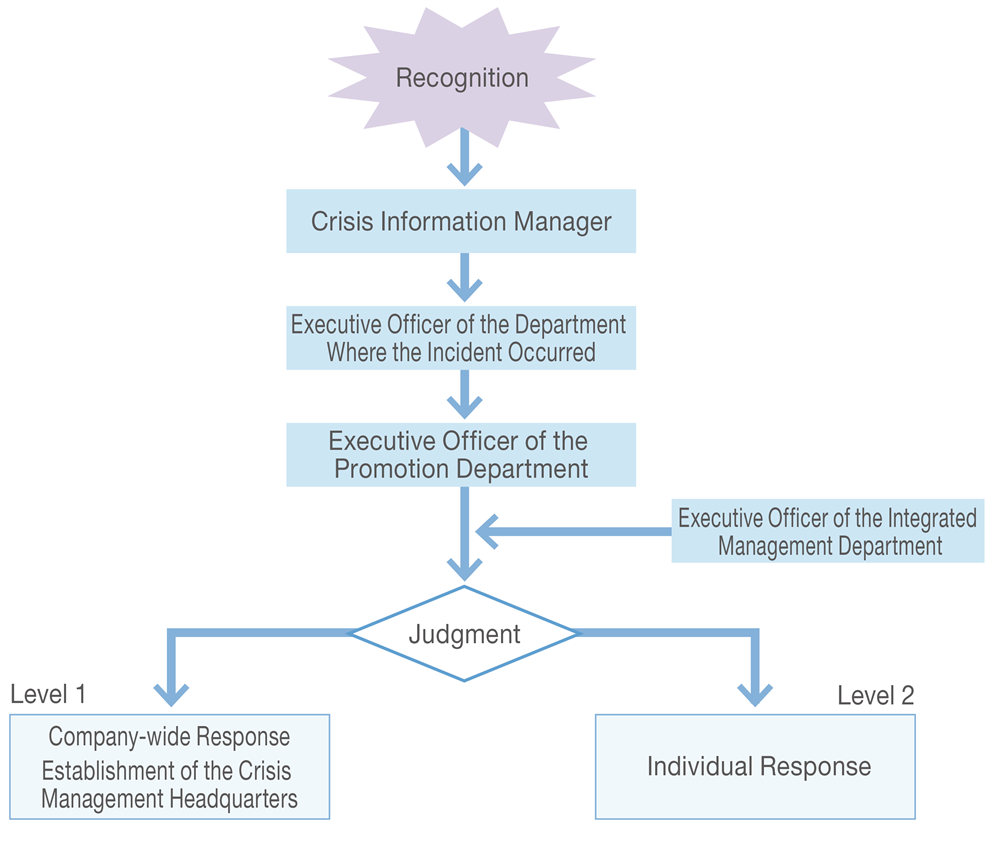
When an emergency situation involving life safety or incidents/accidents affecting management occurs, the crisis information manager of the department where the incident occurred promptly reports to the Executive Officer in charge of that department. The Executive Officer who receives the report consults with the Executive Officer in charge of the relevant risk promotion department and the Executive Officer in charge of risk management oversight, and determines the crisis response level based on the degree of impact on management. Cases where the impact on management is deemed extremely significant are classified as Level 1, and the Crisis Management Headquarters is established at the Head Office to implement comprehensive response measures led by management. Cases where the degree of impact on management is judged not to reach Level 1 are classified as Level 2, and swift, agile responses are carried out by the department where the incident occurred in collaboration with the relevant promotion department.
■Decision-Making Process in Emergency Situations
Crisis Management Headquarters Drill
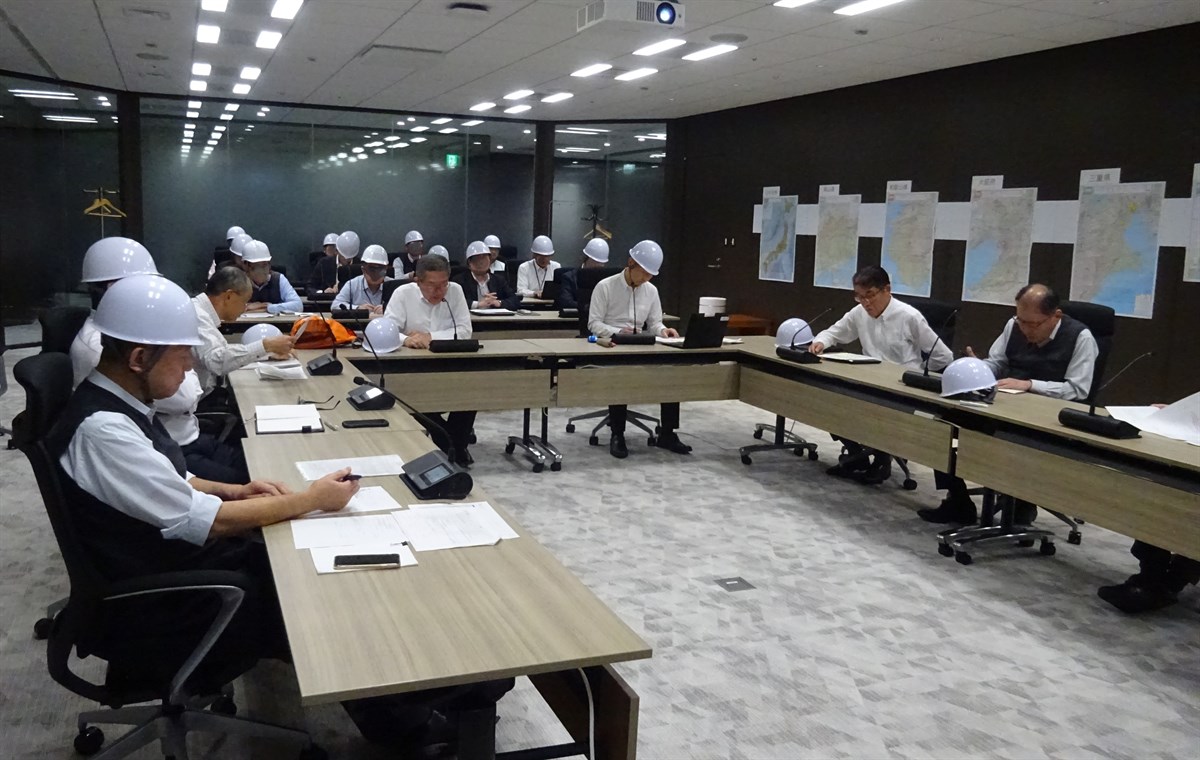
NTN positions the establishment of a structure capable of swiftly and accurately executing initial response measures while demonstrating early post-disaster resilience even in the event of a major management risk such as a large-scale earthquake as a critical management issue. As part of this effort, we conducted the Crisis Management Headquarters Drill with the participation of the President, all Executive Officers, and the heads of relevant departments. In this drill, we simulated the occurrence of an earthquake with a seismic intensity of 7 and established the Crisis Management Headquarters through the crisis response level determination process based on the decision-making process for emergency situations described above. While prioritizing the safety of employees, we carried out practical response activities, including safety confirmation and assessment of damage conditions. By having decision-makers, including top management, personally experience crisis response, we verified the speed of decision-making in emergencies and the effectiveness of the governance structure related to business continuity. Issues identified through the drill will be reflected in revisions to regulations and procedures, and we will continue to pursue ongoing improvements. Through these efforts, we are working to reduce the risk of damage to corporate value in the event of a major disaster and to strengthen our business continuity capabilities.
■Drill in progress
Promotion of BCP/BCM
We have been developing a BCP/BCM structure designed to respond to major earthquakes in Japan and are working to strengthen our disaster response systems, including those of our group companies. We have completed the formulation of BCPs to enable rapid recovery at all production sites across Japan. Based on our experience from the Noto Peninsula Earthquake in 2024, we are carrying out BCP training on an ongoing basis. Furthermore, we have systematically organized the response processes from the occurrence of a disaster through to recovery, and are leveraging these in our BCM activities to enhance our emergency response capabilities and ensure the stability of our business over the medium term.
Strengthening Information Security
Strengthening the CSIRT Structure / Global Deployment of Security Measures
In response to increasing risks of cyberattacks and data breaches and in view of the importance of information security today, we have established a Basic Policy of Information Security alongside our Environment Policy, Human Rights Policy, Safety and Health Basic Policy, and Procurement Policy as one of the NTN Group’s basic policies set forth under our Management Policy.
(Information Security Basic Policy can be found here)At NTN, the Executive Officer in charge of the ICT Strategy Department has overall responsibility for information security, overseeing strategy, operations, and incident response, and reports directly to the Board of Directors. For information security oversight functions, we have established a structure in which the Risk Management Committee, headed by an Executive Officer as General Manager, reports to the Board of Directors. The Board of Directors supervises regular reports on cyber risks, major incidents, and related matters.
Cyberattacks are becoming more complex and sophisticated each day, with numerous similar incidents and information breaches occurring at other companies. When information security incidents occur, it is essential to respond swiftly from detection through reporting to handling of information security risks. We have established a cross-departmental emergency response system for handling information security risks (NTN-CSIRT: NTN Computer Security Incident Response Team), and are working to establish unified security governance across the entire Group through the development and deployment of regional CSIRTs (NTN-REGIONAL-CSIRT). We have begun operations in conjunction with a dedicated security organization (SOC: Security Operation Center) that monitor for cyberattacks 24 hours a day, 365 days a year for early detection.
Furthermore, as part of personnel security measures, we regularly conduct incident response trainings that assume the occurrence of information security incidents, training for dealing with suspicious emails, and e-learning programs to deepen understanding of information security-related regulations and how to deal with information security threats.
[Objectives of Establishing the Computer Security Incident Response Team (NTN-CSIRT)]
(1) Detect information security risks and accelerate communication, reporting, handling, and recovery in the case of risk occurrence
(2) Reduce the risk of information security incidents and prevent them from occurring
(3) Strengthen governance to improve overall information security standards